Governance
Configure fix approvals, protected paths, and account settings in one place.
Research
What Sandboxie CVE-2025-64721 teaches about length validation, allocation arithmetic, and sandbox trust boundaries.
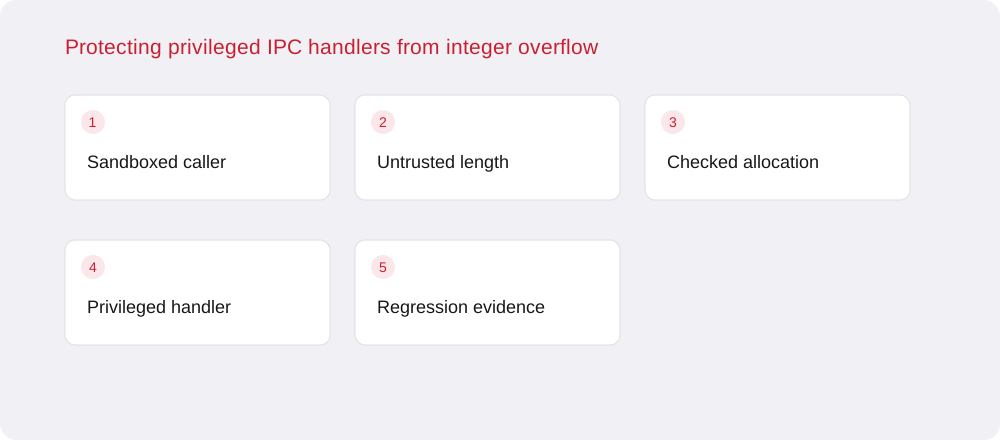
A sandboxed process often needs to ask a more privileged service to perform a narrow operation. That service becomes part of the isolation boundary. It must treat every message field as untrusted even when the caller is a legitimate sandboxed application and the transport is an operating-system IPC mechanism.
CVE-2025-64721 concerns Sandboxie's privileged SbieSvc service. The upstream advisory identifies unchecked size arithmetic in an SbieIniServer handler that can lead to an undersized allocation and a subsequent heap overwrite. This is an application service boundary issue; the identifier should not be described as a generic Windows kernel vulnerability.
A length field needs several checks, not just a nonnegative value. The received message must contain the advertised bytes, the requested operation must permit that length, and adding headers or multiplying element counts must remain representable in the allocation type. Validation performed after arithmetic has already wrapped cannot recover the intended size.
Use checked arithmetic or a precondition that proves the complete calculation safe. Keep units explicit: byte counts, character counts, and element counts are not interchangeable. When a handler copies data after allocating a header plus payload, both operations should use the same validated size contract.
Review alternate handlers, compatibility paths, and error responses rather than assuming that one validation helper protects the service. A caller may reach the same allocation through different operation codes. Also inspect conversions between signed and unsigned values and between wire-format integers and native platform types.
The check belongs at the privileged boundary, before it acts on the caller's data. A client library can provide additional validation for usability, but a compromised client can avoid that library. Authorization of the requested operation and validation of its memory representation are separate obligations.
An isolated regression test can submit length values around the permitted maximum and verify that the handler returns a defined error without allocating or copying outside its bounds. Include inconsistent message lengths, empty inputs, repeated requests, and cancellation. Instrumented builds can help identify the specific invariant that a test violates.
Confirm that the service remains available after rejection and that another client cannot observe leftover data. These checks establish robust error handling without needing a complete sandbox-escape chain. A crash is already sufficient reason to investigate the memory boundary; it is not necessary to demonstrate host takeover in routine validation.
The Sandboxie advisory lists version 1.16.7 as the fix boundary for this issue. Operators should check their installed service and driver package against maintained vendor releases, rather than assuming that updating a user-facing executable replaced every component. Restart requirements and long-running service instances matter when verifying rollout.
Keep least privilege and service isolation as defense in depth, while recognizing that a SYSTEM-level helper has substantial authority by design. Record the affected product, service revision, patch evidence, and regression result precisely. Do not infer that every Windows application using local IPC shares this particular vulnerability.
Configure fix approvals, protected paths, and account settings in one place.
Review findings and fix activity in one place, with finding exports available.
Review recorded scan activity and finding state changes.
Account membership controls access to connected repositories and findings.
Bring your own encryption key. Your data stays encrypted with keys you control.