Built on Counterswarm’s agentic defense system.
Counterswarm investigates package risk using dependency evidence and security analysis.
Package protection designed for supported, configured installation paths. Deployment scope and availability depend on the integration.
Counterswarm investigates package risk using dependency evidence and security analysis.
An intended deployment pattern places Dependency Firewall upstream of a private registry or artifact repository. Inspection coverage depends on supported integrations and configured package paths.
An intended deployment pattern reviews package requests from supported endpoints. Coverage depends on routing those requests through the configured integration.
Dependency Firewall is intended to review package requests from developer and AI-agent environments when they use a supported, configured installation path.
Assess package risk before introducing a dependency into your environment.
Define package review criteria for your team. Available enforcement depends on the integration, configured policy, and installation paths in scope.
Define what your company will accept, from package attributes to license terms. Require a minimum package age, gate specific dependency trees, and enforce license policies across direct and transitive dependencies.
Share findings with your team through configured notifications and finding exports.
Define a review and exception process for package decisions.
Consider package review as part of your dependency installation workflow.
Find real vulnerabilities by tracing business logic, data flows, and cross-service interactions across your codebase.
Counterswarm investigates business logic and data flows, prioritizing findings with supporting evidence.
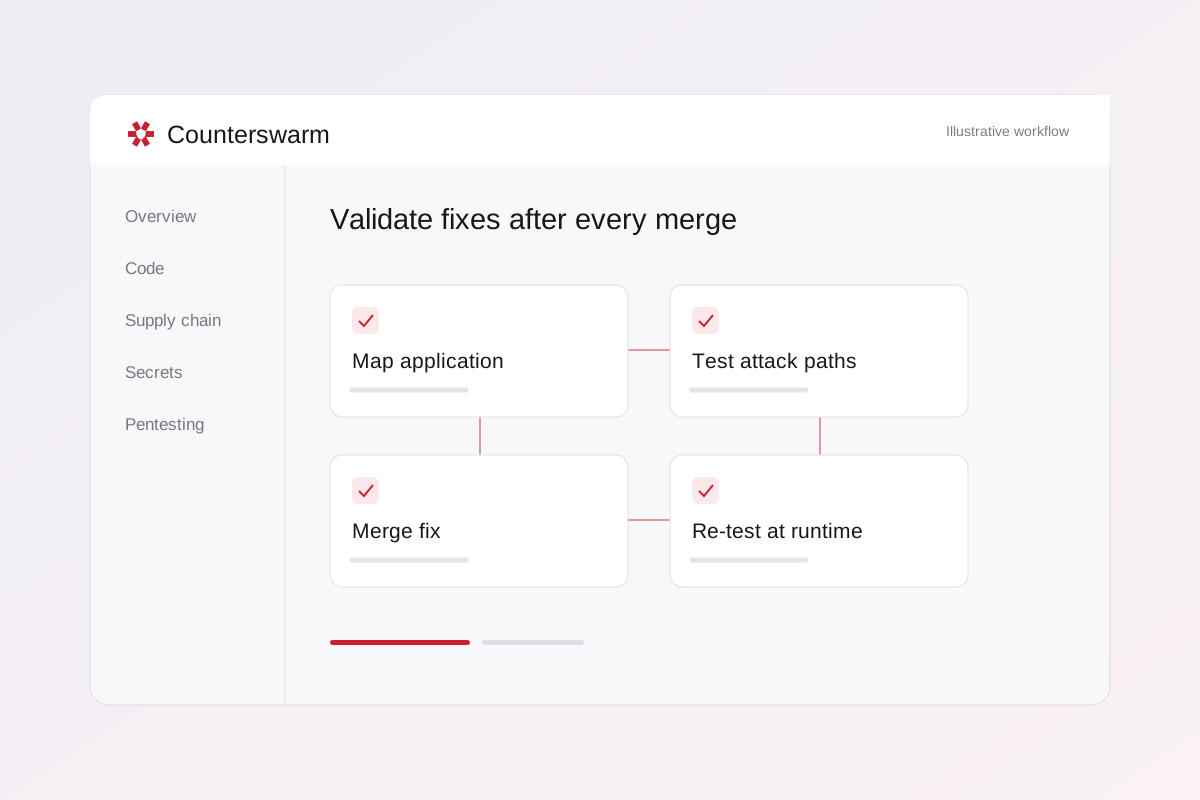
Confirm which vulnerabilities are exploitable by testing your running application with real attack paths.
Counterswarm tests your running applications and automatically re-tests fixes at runtime after every merge.
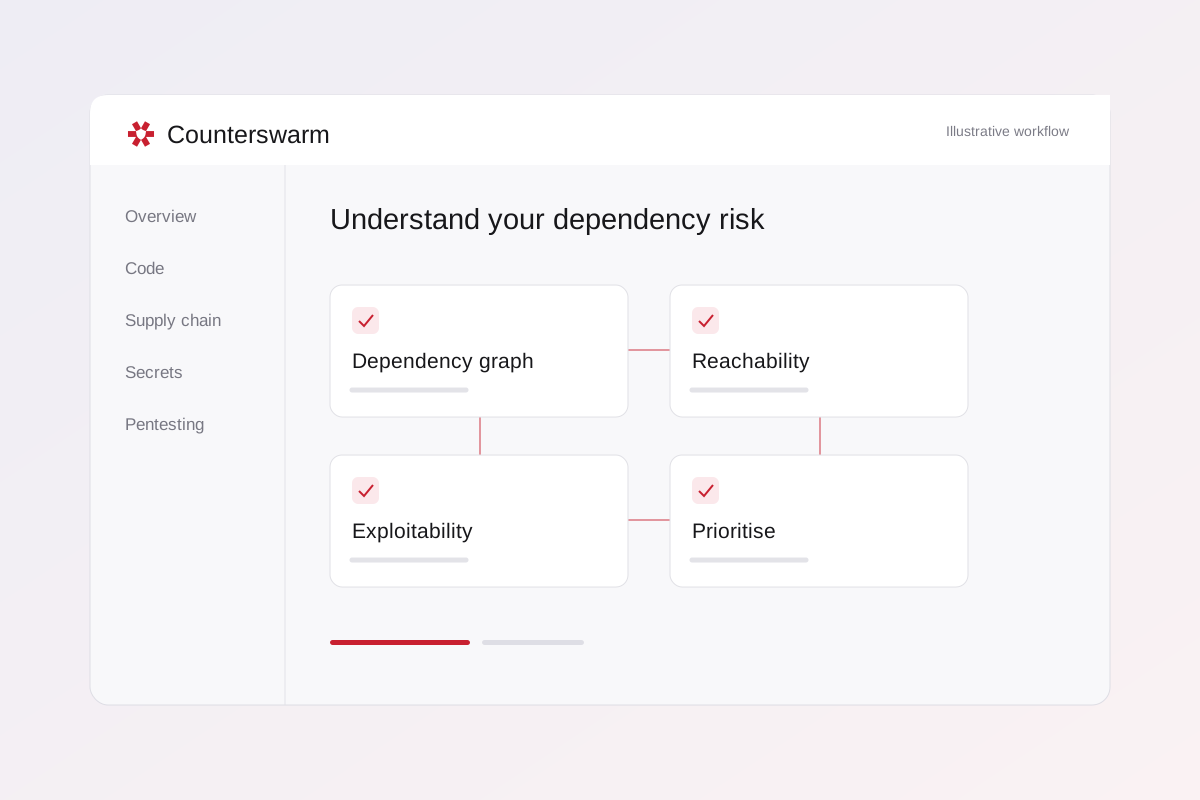
Prioritize dependency risk using package versions, advisories, and available usage evidence.
Counterswarm uses dependency versions and import evidence to help prioritize vulnerabilities relevant to your application.
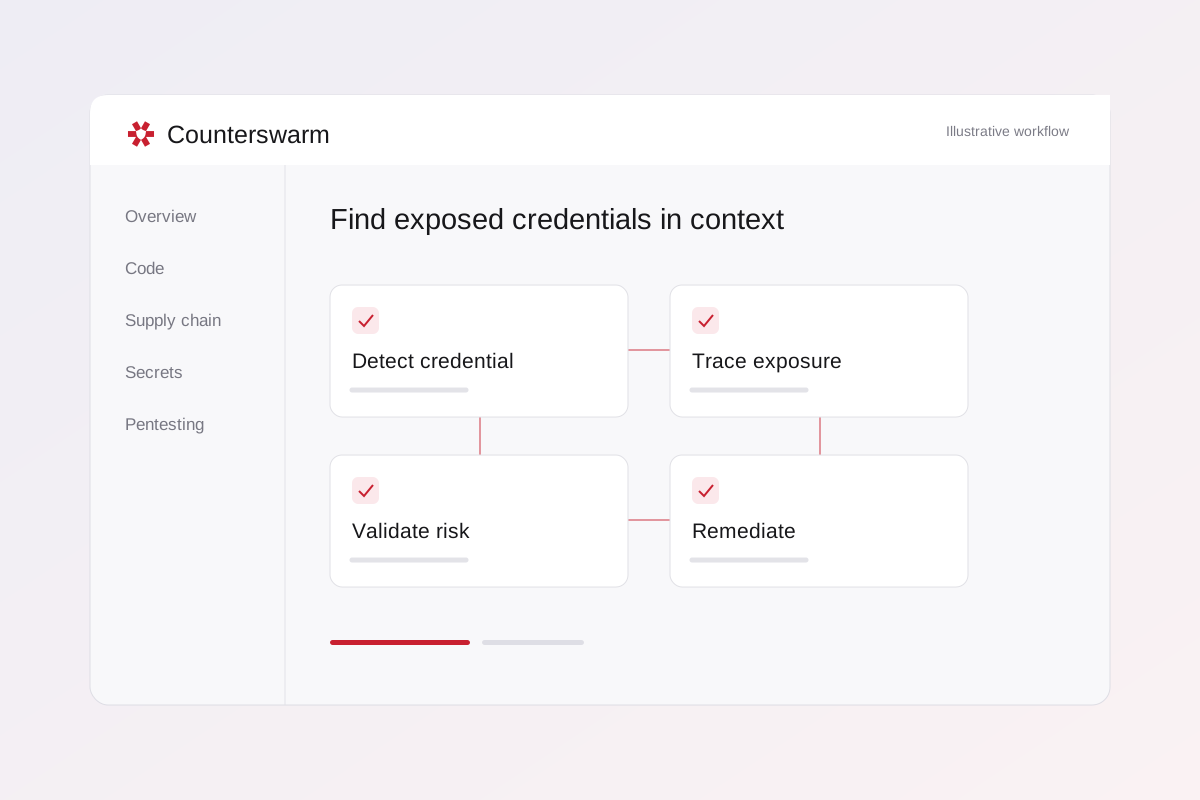
Detect and validate credentials across your codebase, CI/CD pipelines, and runtime environments.