Prompt injection vulnerabilities
Tests whether AI-powered features execute injected instructions by manipulating inputs across user-facing and backend prompts. Findings show the injection path and model response.
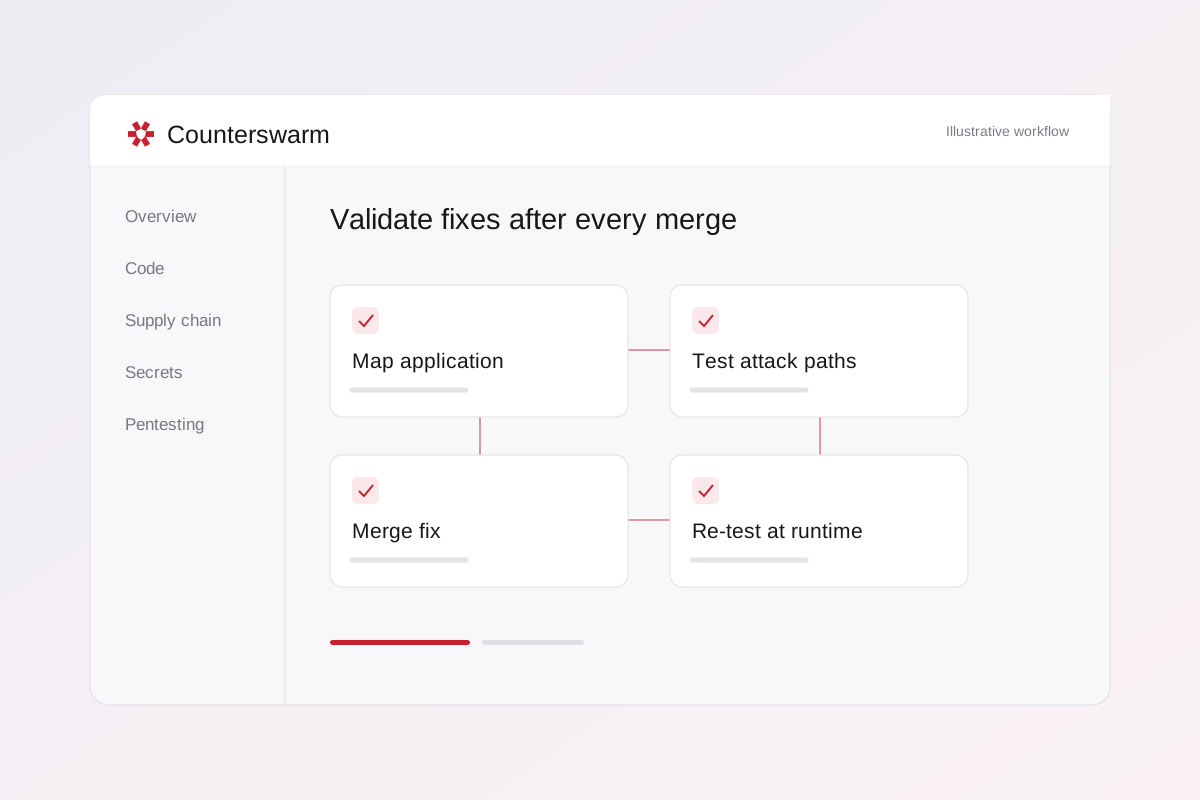
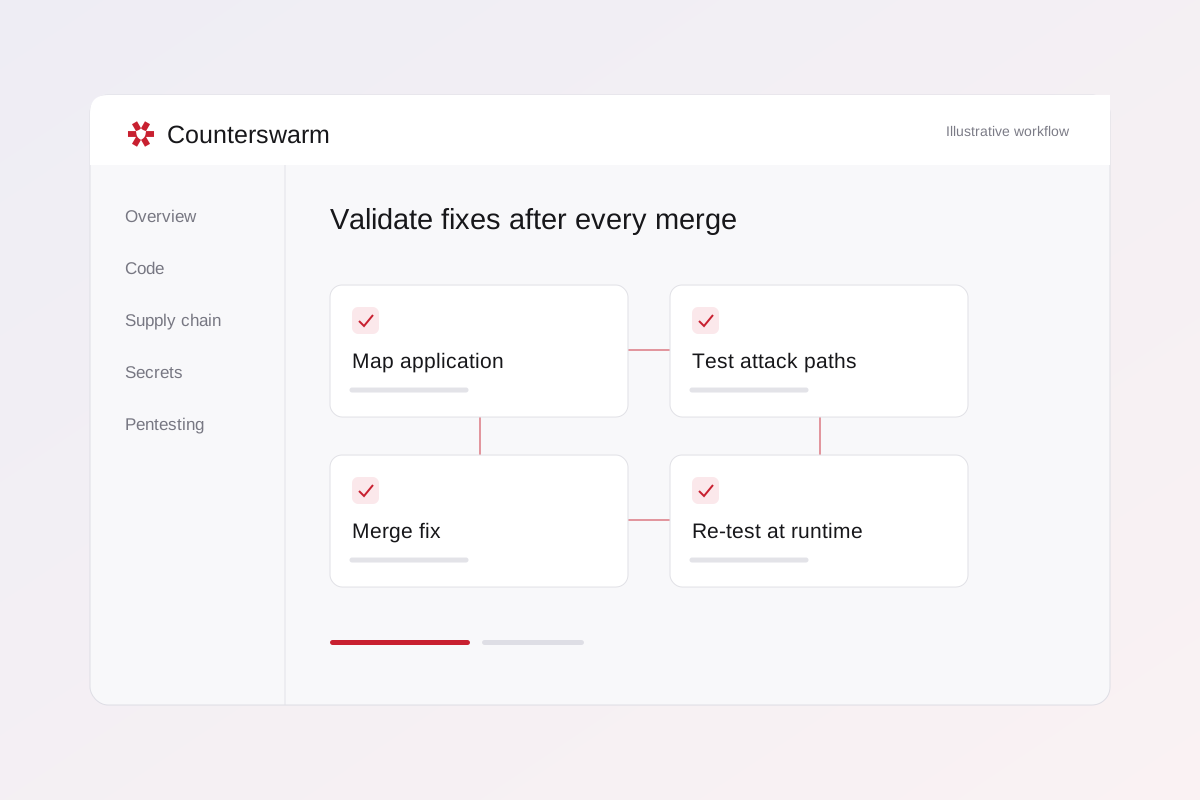
Investigate vulnerabilities in your running applications and automatically re-test fixes at runtime after every merge.
Tests whether AI-powered features execute injected instructions by manipulating inputs across user-facing and backend prompts. Findings show the injection path and model response.
Tests whether users can access data that doesn’t belong to them by modifying object identifiers in real requests and checking for unauthorized responses.
Counterswarm maps how weak points connect through your application’s data flows and control logic to surface exploitable vulnerability chains.
AI agents authenticate, navigate UI and APIs, and chain requests to execute real attack paths against your running application.
Findings from code, supply chain, secrets, and infrastructure are tested at runtime. Confirmed vulnerabilities include a unified timeline of static evidence and dynamic exploitation.
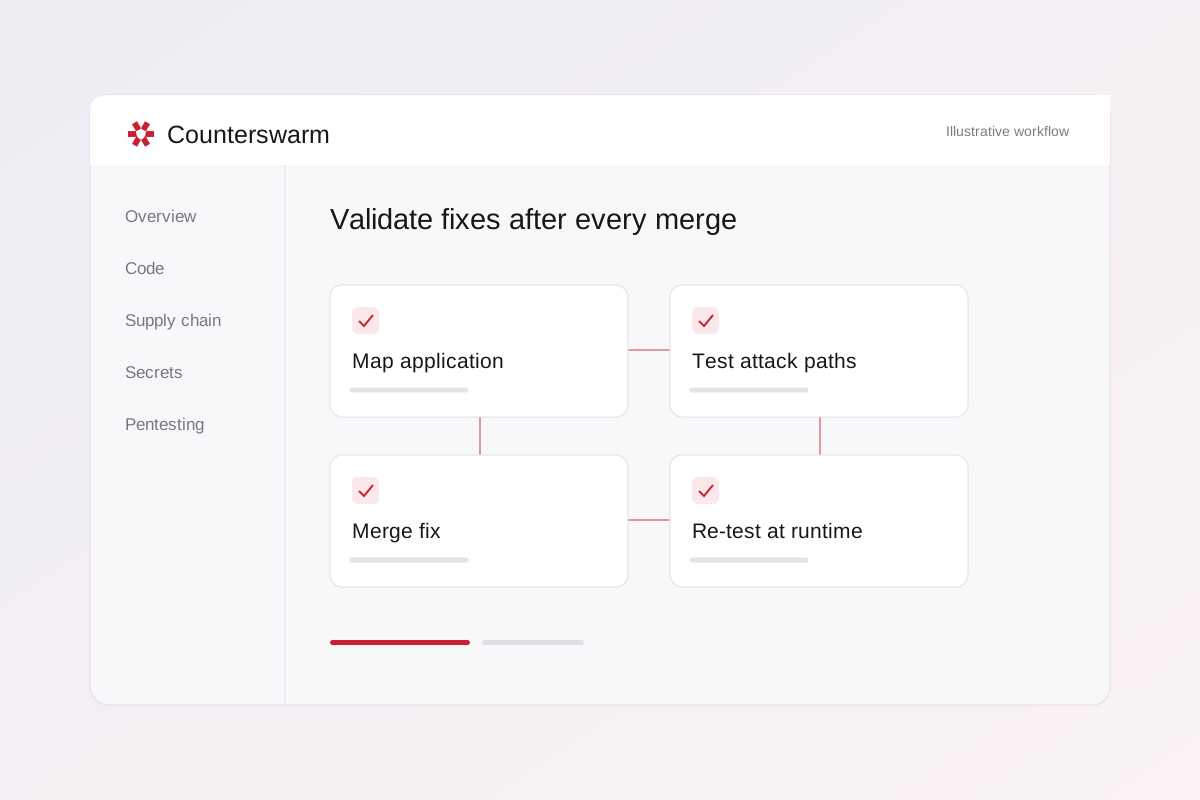
Counterswarm automatically replays runtime tests after every merge to verify that fixes address the reported issue.
Run white-box tests informed by full code context, grey-box tests with partial access, or black-box tests against any URL or API endpoint.
Agentic pentests re-run automatically after every merge to verify fixes in your running application.
Static findings are linked to dynamic exploitation attempts in a single timeline, showing both the code-level evidence and the runtime result.
Support a wide range of authentication methods and test across multiple scoped roles to reflect real user access.
Find real vulnerabilities by tracing business logic, data flows, and cross-service interactions across your codebase.
Counterswarm investigates business logic and data flows, prioritizing findings with supporting evidence.
Detect malicious behavior before it spreads through your environment.
Prioritize dependency risk using package versions, advisories, and available usage evidence.
Counterswarm uses dependency versions and import evidence to help prioritize vulnerabilities relevant to your application.
Detect and validate credentials across your codebase, CI/CD pipelines, and runtime environments.